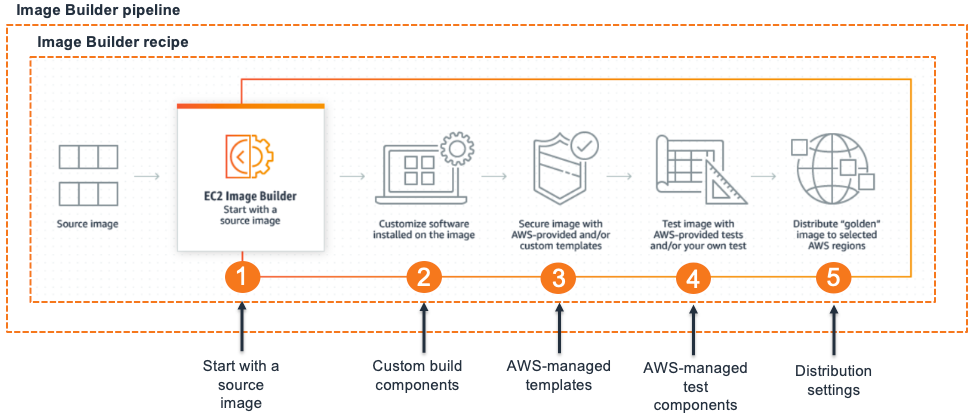
What it is:
- AWS service to automate building, testing, and distributing secure "golden" AMIs (and container images).
- Helps maintain up-to-date, patched, hardened machine images.
Key Concepts:
- Image Pipeline: The full automated workflow (build, test, distribute).
- Image Recipe: Defines the base image (e.g., Amazon Linux 2023) and components (build/test steps).
- Components: Reusable scripts/configs (YAML) for installing software, patching, hardening, testing. AWS provides many; you can create custom.
- Infrastructure Config: Specifies the EC2 instance type, subnet, security group, IAM role for the build process.
- Distribution Config: Defines where to send the final image (Regions, accounts/OUs, tags, KMS keys for encryption).
- Versioning: Recipes and components use semantic versions (1.0.0).
How it Works (Simple Flow):
- Start: Pipeline triggered (schedule or base image update).
- Build: Image Builder launches a temporary EC2 instance.
- Apply Recipe: Runs build components (installs, configures, patches).
- Create Image: Creates the AMI (and underlying snapshots).
- Test: Launches another temporary instance, runs test components.
- Distribute: If tests pass, copies/shares the AMI to specified Regions/accounts.
- Clean Up: Terminates temporary instances.
Use Cases:
- Creating Golden AMIs for consistent deployments.
- Automated patching (e.g., monthly security updates).
- Multi-region image distribution.
- Building images with pre-installed agents (SSM, monitoring).
- Ensuring compliance (CIS benchmarks, vulnerability scans).
Benefits:
- Automation: Reduces manual effort and human error.
- Consistency: Ensures all images are built the same way.
- Security: Integrates hardening, testing, and encryption.
- Scalability: Distribute images across many accounts/regions easily.
- Cost-effective: Pay only for build resources used.
Security Features
- Encrypted AMIs with customer KMS keys
- Compliance testing (CIS, custom scans)
- Least privilege IAM roles
- Audit trails via CloudTrail